About Rietta Cybersecurity
Rietta, Inc. is a cybersecurity firm. We provide security and document accessibility audits, attestation, and process advisory services for governments and regulated SaaS companies. We are engaged to independently verify, not just build, that critical systems and documents meet real compliance standards. We’re trusted by state court agencies and other regulated clients who need that independence to mean something.
We also have a long history of training and educational content, teaching developers and the organizations around them how to build security in from the start, not bolt it on after the fact.
ADA Title II & WCAG 2.1 Conformance Auditing
Yes, a cybersecurity firm. Making content accessible to everyone is the goal, but compliance itself is a legal risk management exercise, the same discipline we already apply to cybersecurity. We provide documented ADA Title II and WCAG 2.1 conformance audits, powered by our Metadata Minder platform.
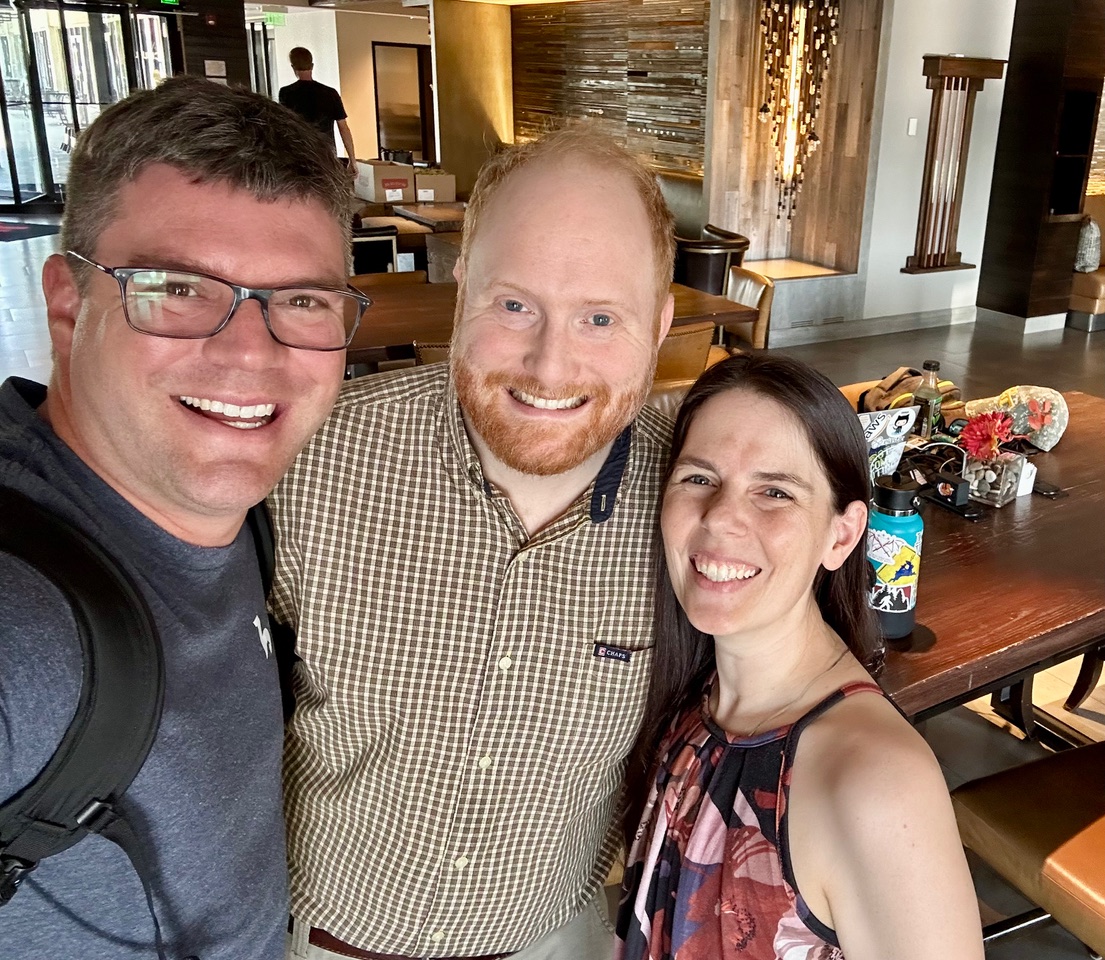
Our Team
Frank Rietta — Founder & CEO

Frank Rietta: 27+ years of security expertise. Computer scientist, OWASP lifetime member. Public speaker on data breaches.
Wren Steitle — Senior Software Developer
Wren is Rietta's Senior Software Developer, responsible for vulnerability management, patch cadence, and code review across our client base.
Sam Rietta — Government Sales Manager
Sam Rietta is Rietta's Government Sales Manager, a career sales engineer bringing decades of experience to our push into government agencies.
Charles Roach — Business Development Manager
Charles Roach is Rietta's Business Development Manager, a serial entrepreneur whose biggest exit was AdThrive, growing revenue from $65K to $25M.
Selected Case Studies
As a cybersecurity firm, most of our clients require confidentiality. These are real engagements, anonymized by agreement.
Saving a State Agency’s Archive of Record
When neither Google nor AWS had a migration path off a sunset platform, we built one.
InsuranceComplex Insurance Document Solution
A purely open source LibreOffice, Docker, and AWS deployment for a regulated document workflow.
Regulated & Air-Gapped SystemsSecuring the Unconnected
A tailored security assessment and developer training program for an air-gapped application.
27 Years in Business
Rietta.com has been online since 1999, and Frank has personally written the Rietta Blog since 2005. Our legacy software archive still has what we built back then, RoboGen, MenuSnap, and Whois Web Professional, if you want to check for yourself. For compliance and security work, that kind of history matters. We’ll be here for your next audit, not just this one.
Mission Statement
Security must be baked in, not bolted on.
How We Work: Five Core Capabilities
The five hexagons in the Rietta logo stand for our five Core Capabilities, the stages of a software system’s life that our work covers. They have matched for over a decade, and they are the foundation under every solution we offer.
- Understand: learning your business, your people, and your requirements before anything is built.
- Develop: building and reviewing software with security in every stage, on technology with a proven track record.
- Secure: threat modeling, security reviews, and remediation, working alongside your own team.
- Operate: cloud architecture and operations with security built in from the start.
- Maintain: security patches, dependency upgrades, and fixes for audit findings, for as long as the software runs.
Remote Native Since Day One
We’ve been remote-native since Rietta started in 1999: phone calls before Skype and screen sharing existed, then video meetings once they did, and never on-site, not even during the years we provided web hosting and development services. Many of our assessments and deliverables don’t require the expense of on-site travel, which keeps costs down for clients without cutting corners on the work. It’s also part of what makes our independent verification independent: we’re not embedded on-site with the client we’re assessing.